Writing archive
AI systems and assurance
Writing on what technology makes possible, how it changes the business and what it takes to make the change real.
-
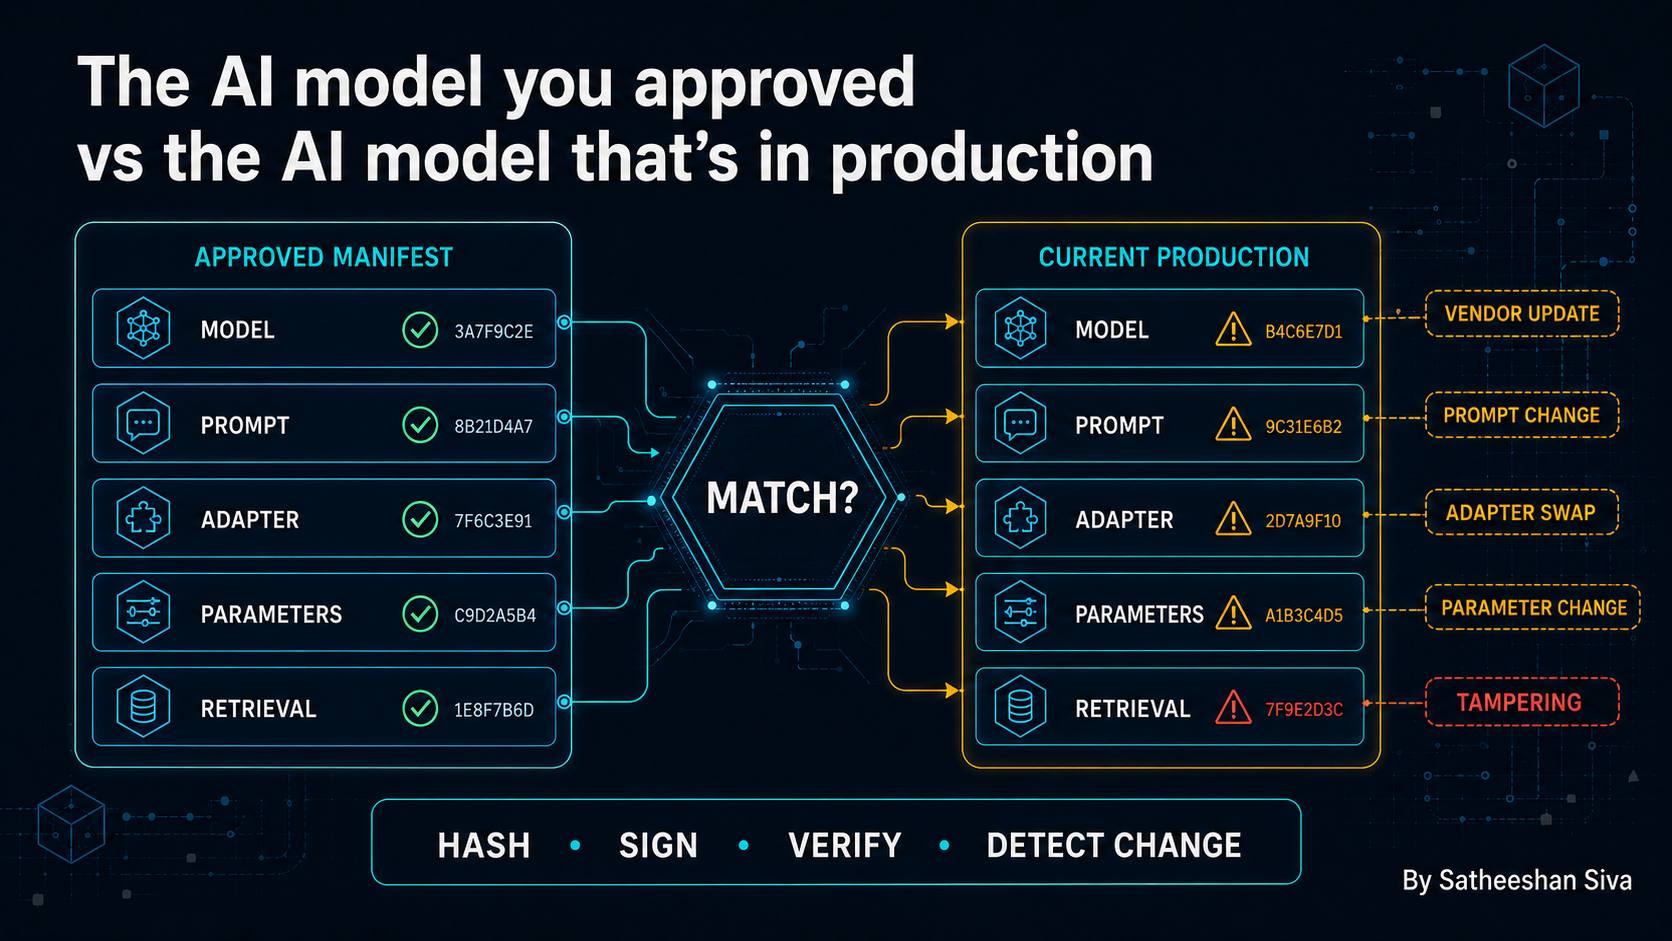
The AI model you approved vs the AI model that’s in production
How component records, signatures and change detection help establish whether the AI system in production is the one that was approved.
-
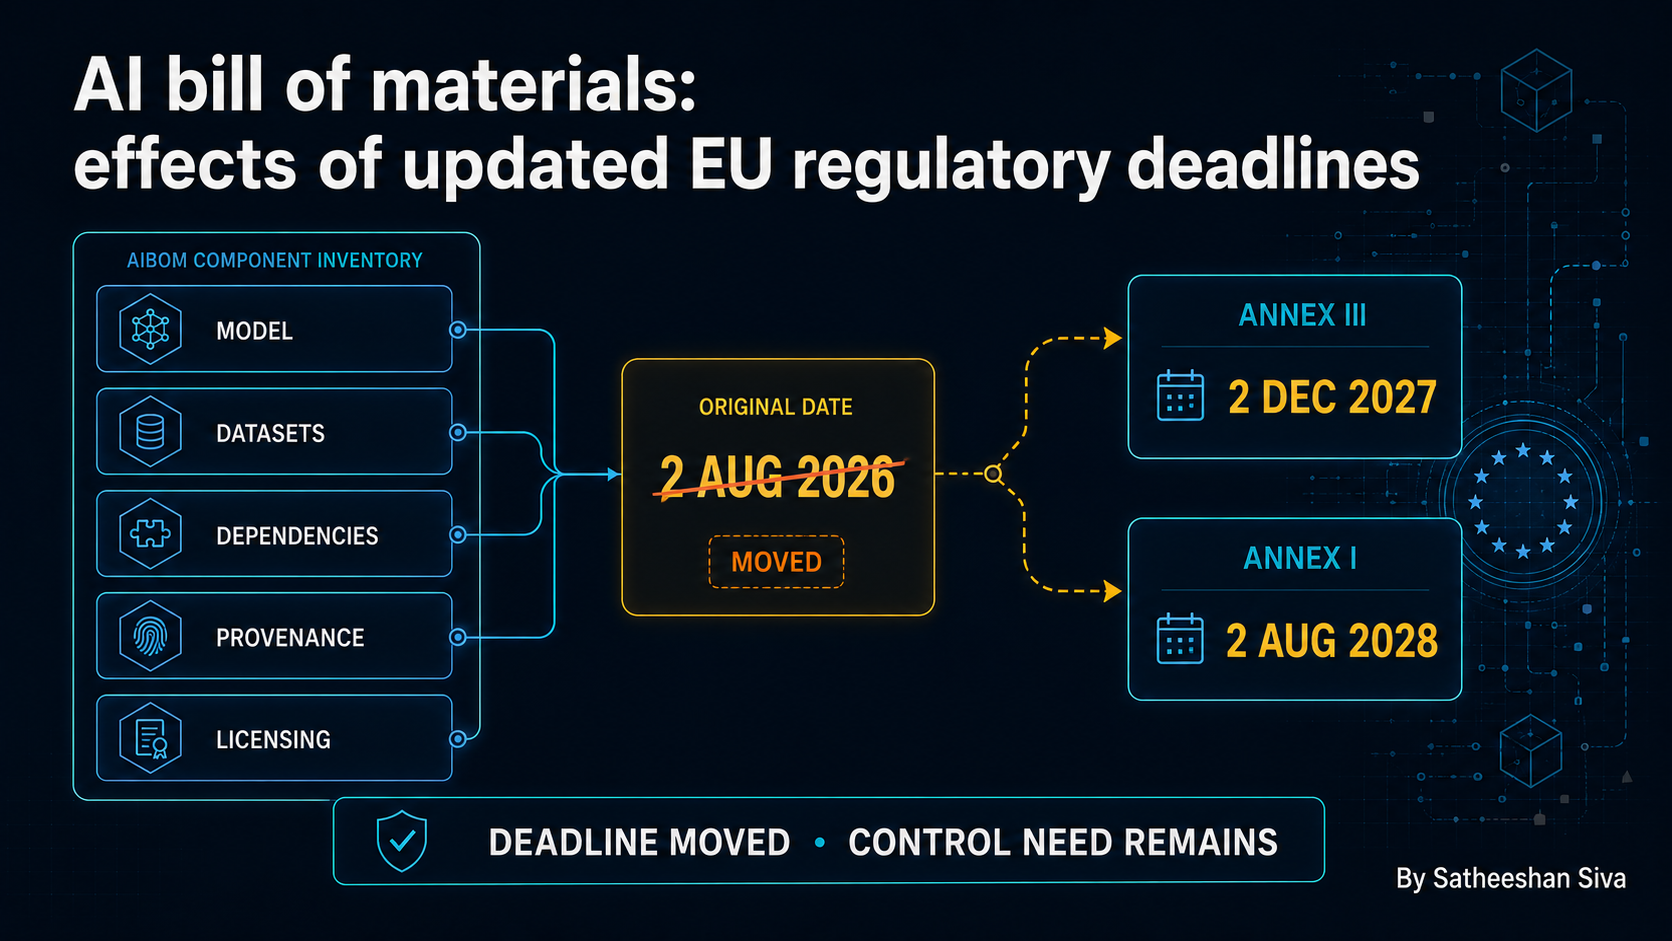
AI bill of materials – effects of updated EU regulatory deadlines
What an AI bill of materials records, and how documentation, assurance and changing regulatory timetables affect the business case for building one.
-

Securing your AI/ML models: signing them with OMS
How OpenSSF Model Signing and Sigstore support model integrity, where signature verification belongs, and why signing and scanning do different jobs.
-
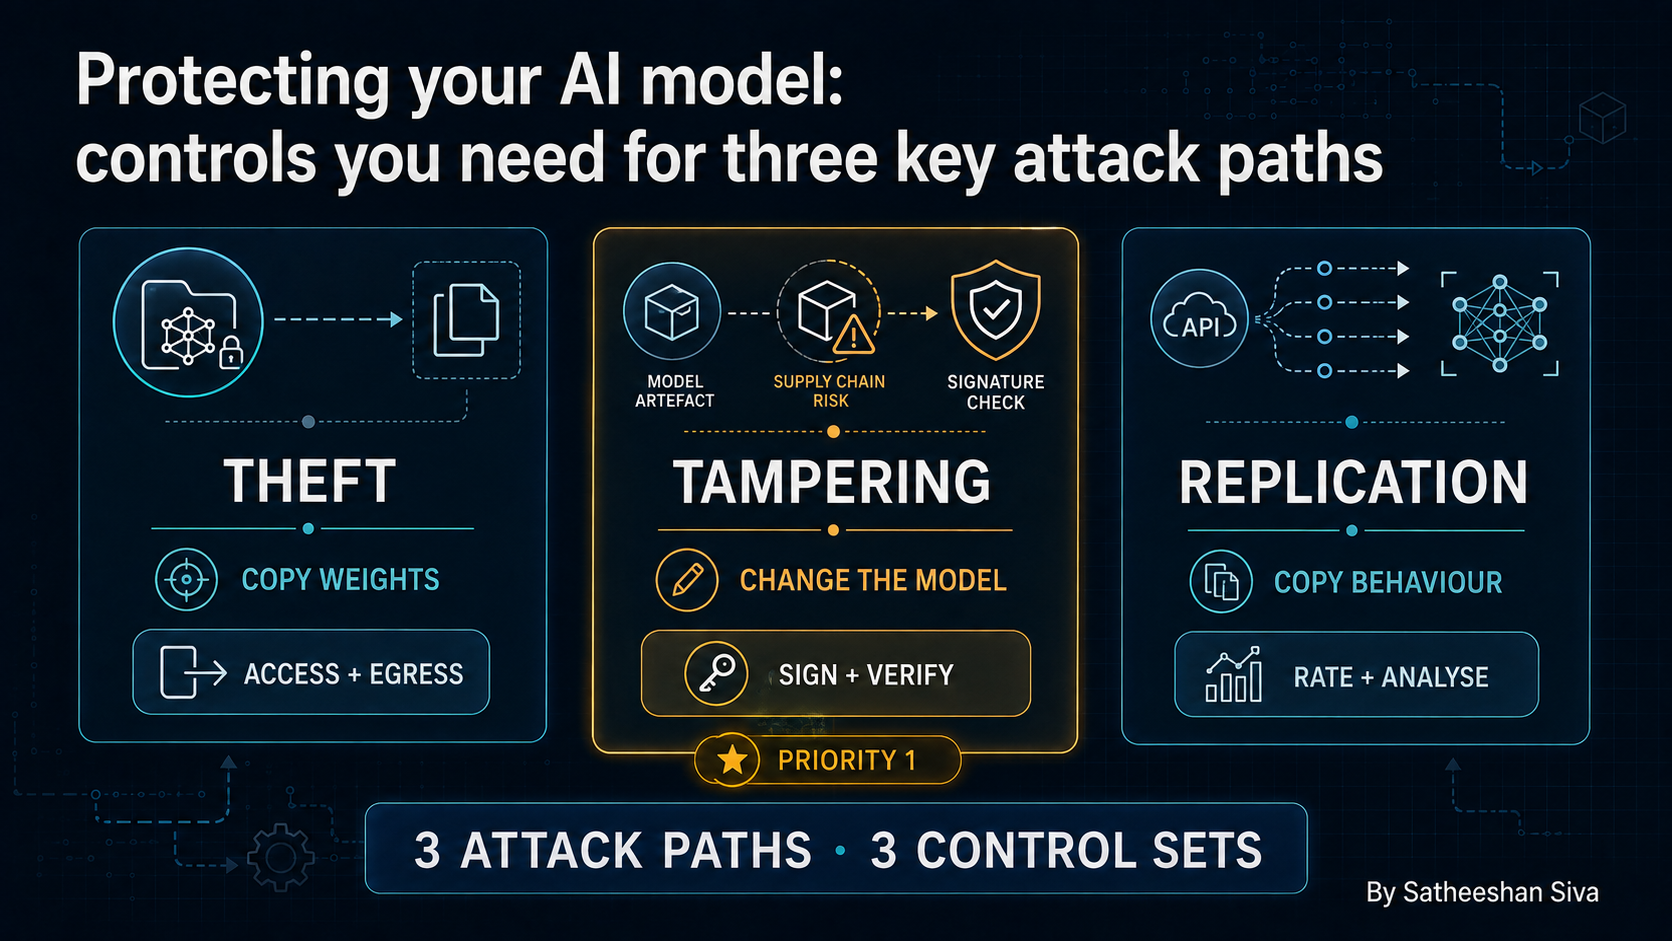
Protecting your AI model: controls you need for three key attack paths
Model theft, tampering and replication create different attack paths. A practical look at the controls and ownership each one needs.
-
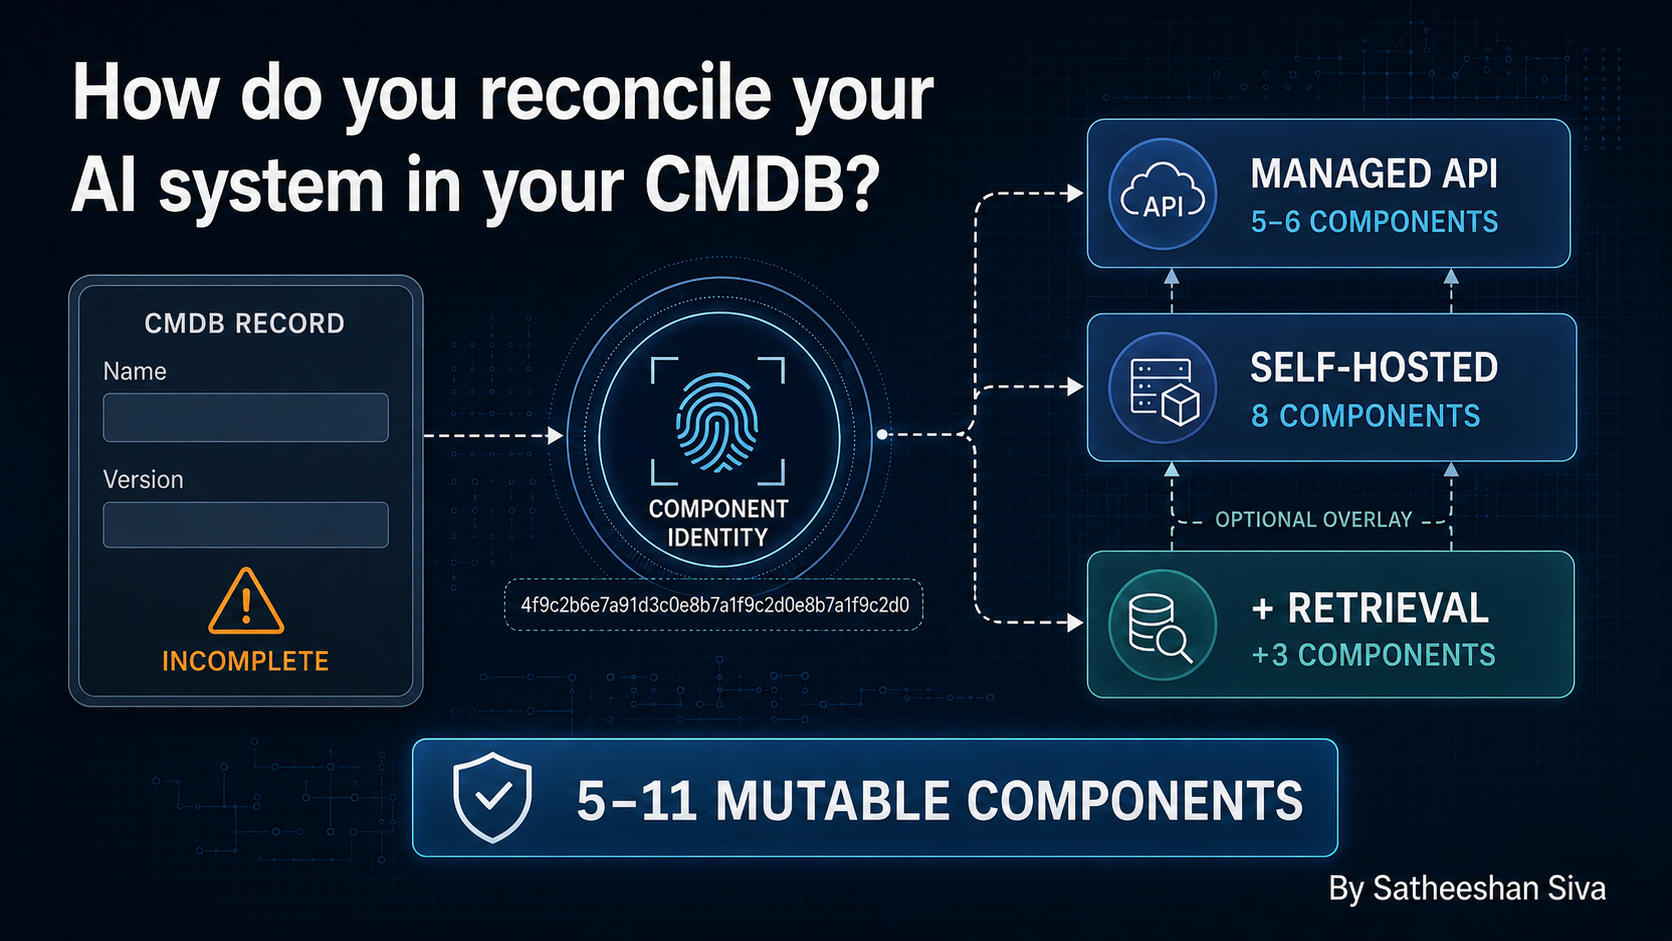
How do you reconcile your AI system in your CMDB?
A working model for recording AI system identity in a CMDB, including components, hashes, provider identifiers and changes beyond the model version.
-
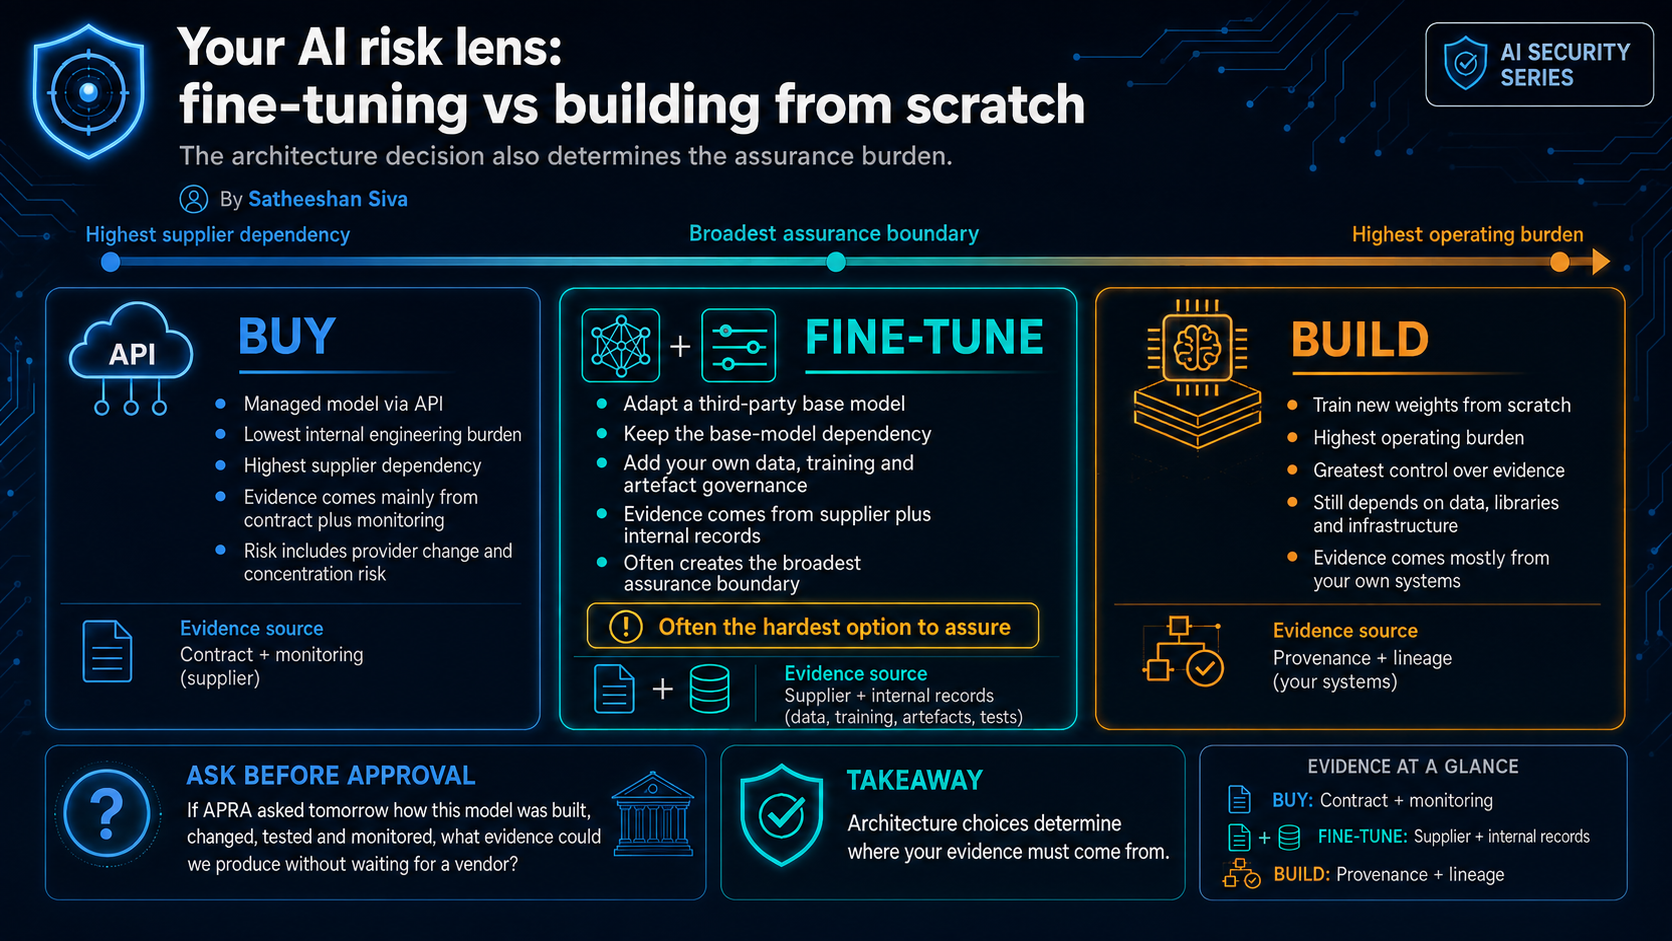
Your AI risk lens: fine-tuning vs building from scratch
Buying, fine-tuning and building AI models create different assurance boundaries. Compare the evidence and responsibilities each architecture requires.
-
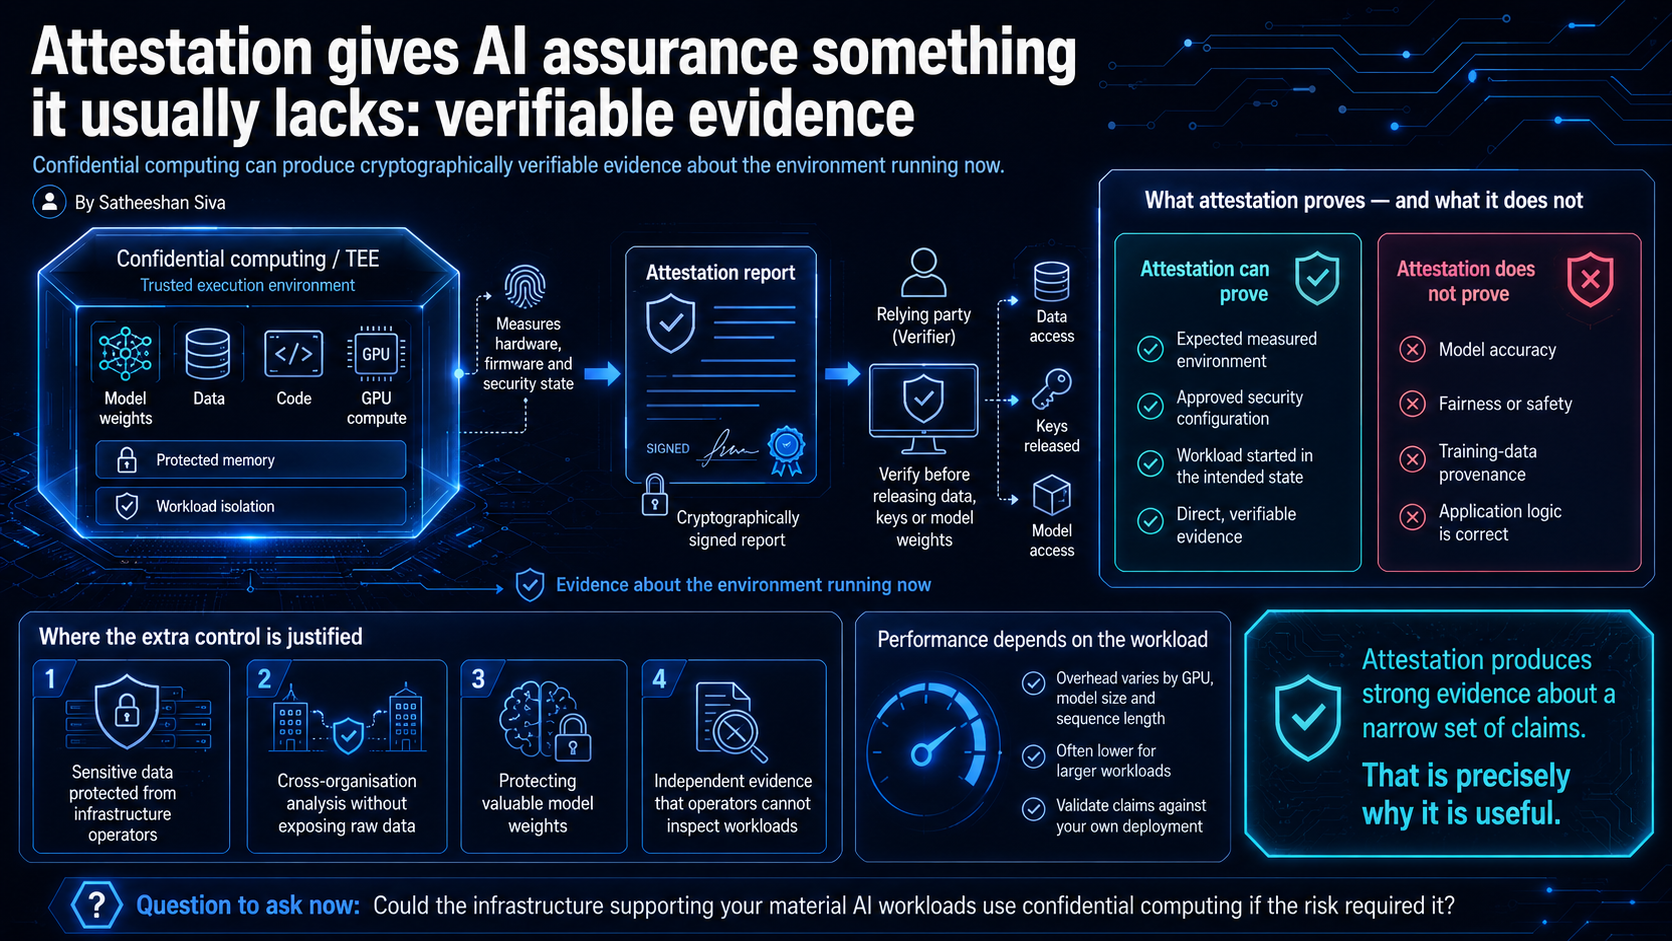
Attestation gives AI assurance something it usually lacks: verifiable evidence
What confidential computing and hardware attestation can add to AI assurance, where the evidence stops and when the additional protection is useful.
-
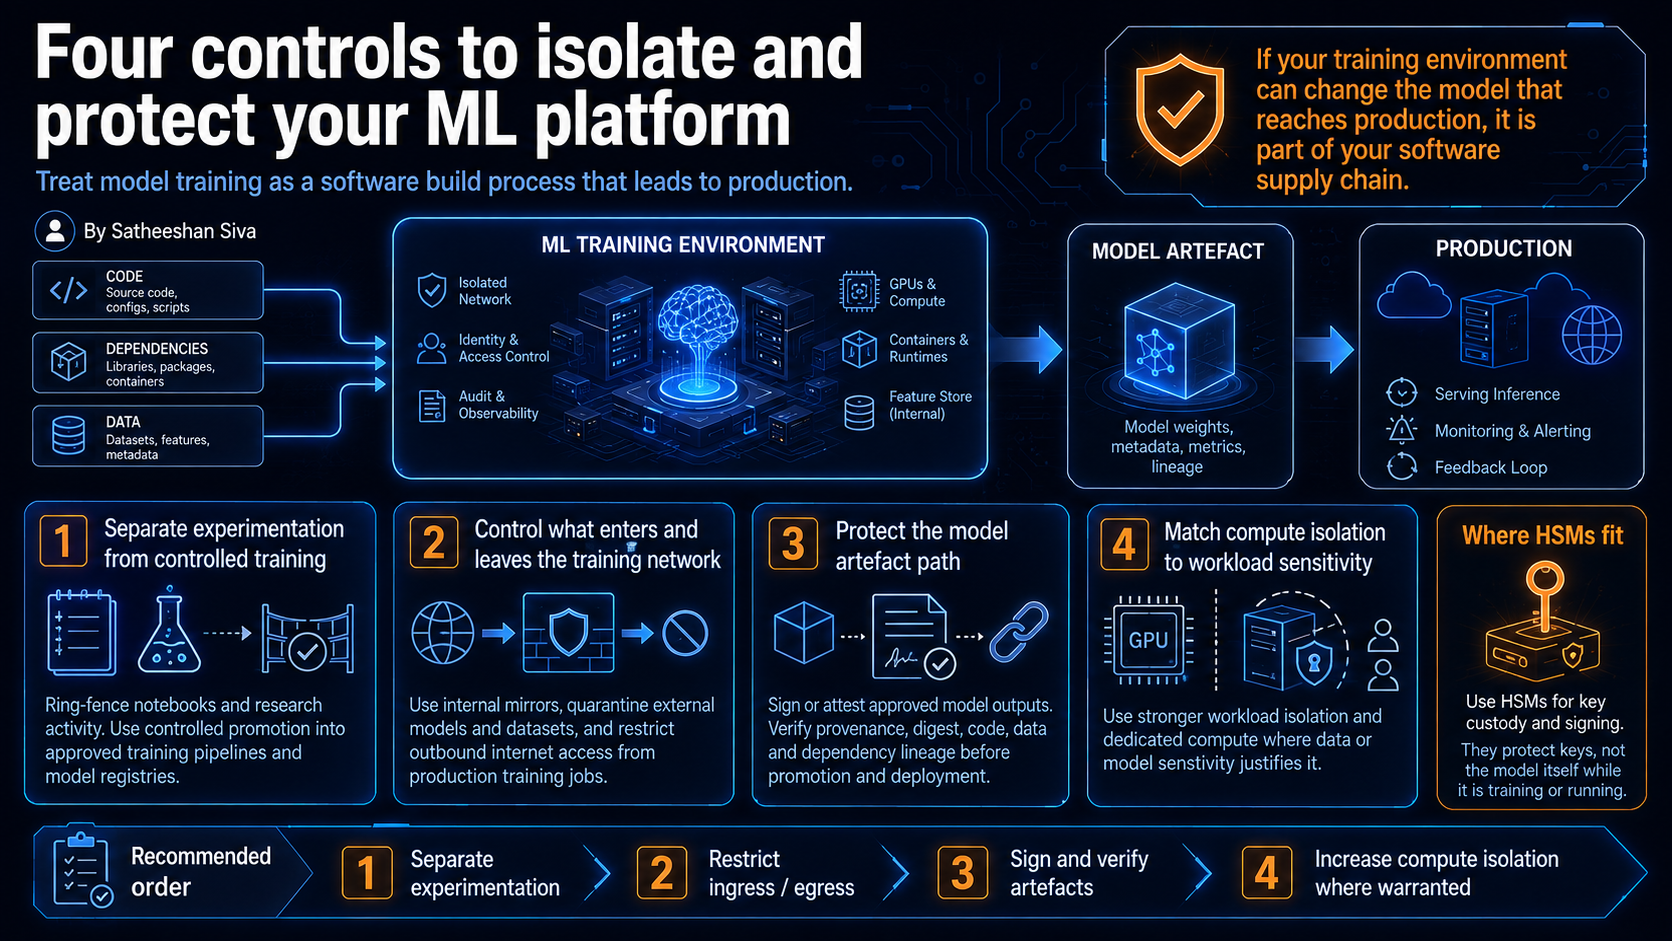
Four controls to isolate and protect your ML platform
Four priorities for protecting an ML platform: separate experimentation, control network access, protect artefacts and match compute isolation to risk.
-
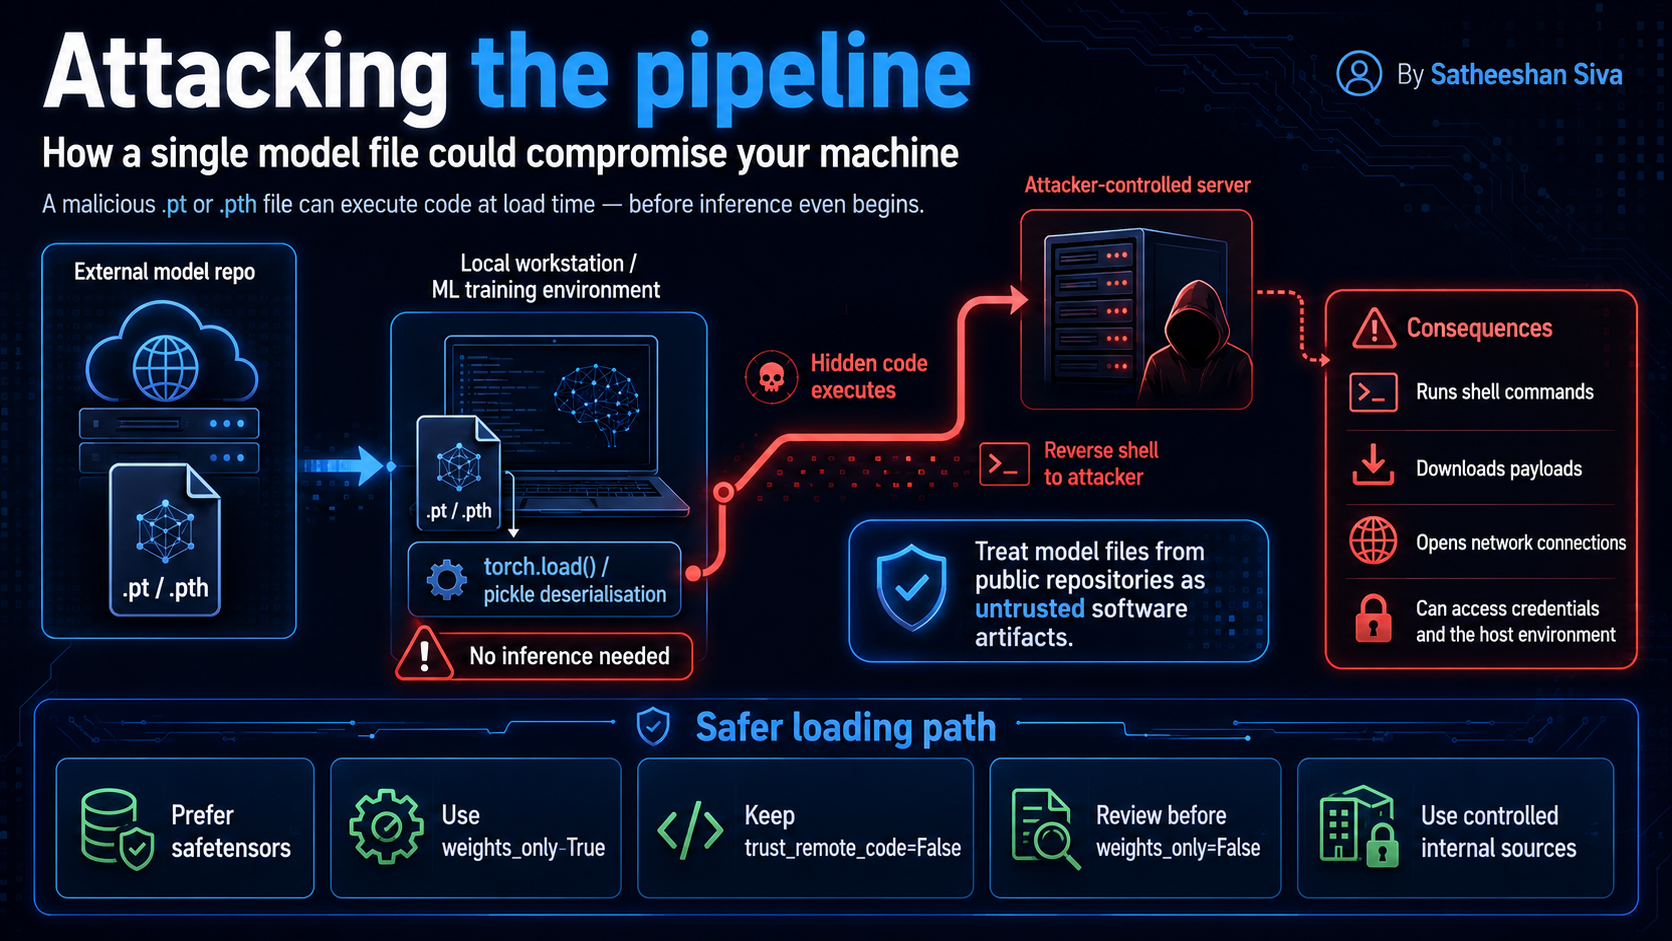
Attacking the pipeline: how a single model file could compromise your machine
How unsafe model-loading paths can execute code, what restricted loading and safer formats change, and why scanning remains only one part of protection.
-
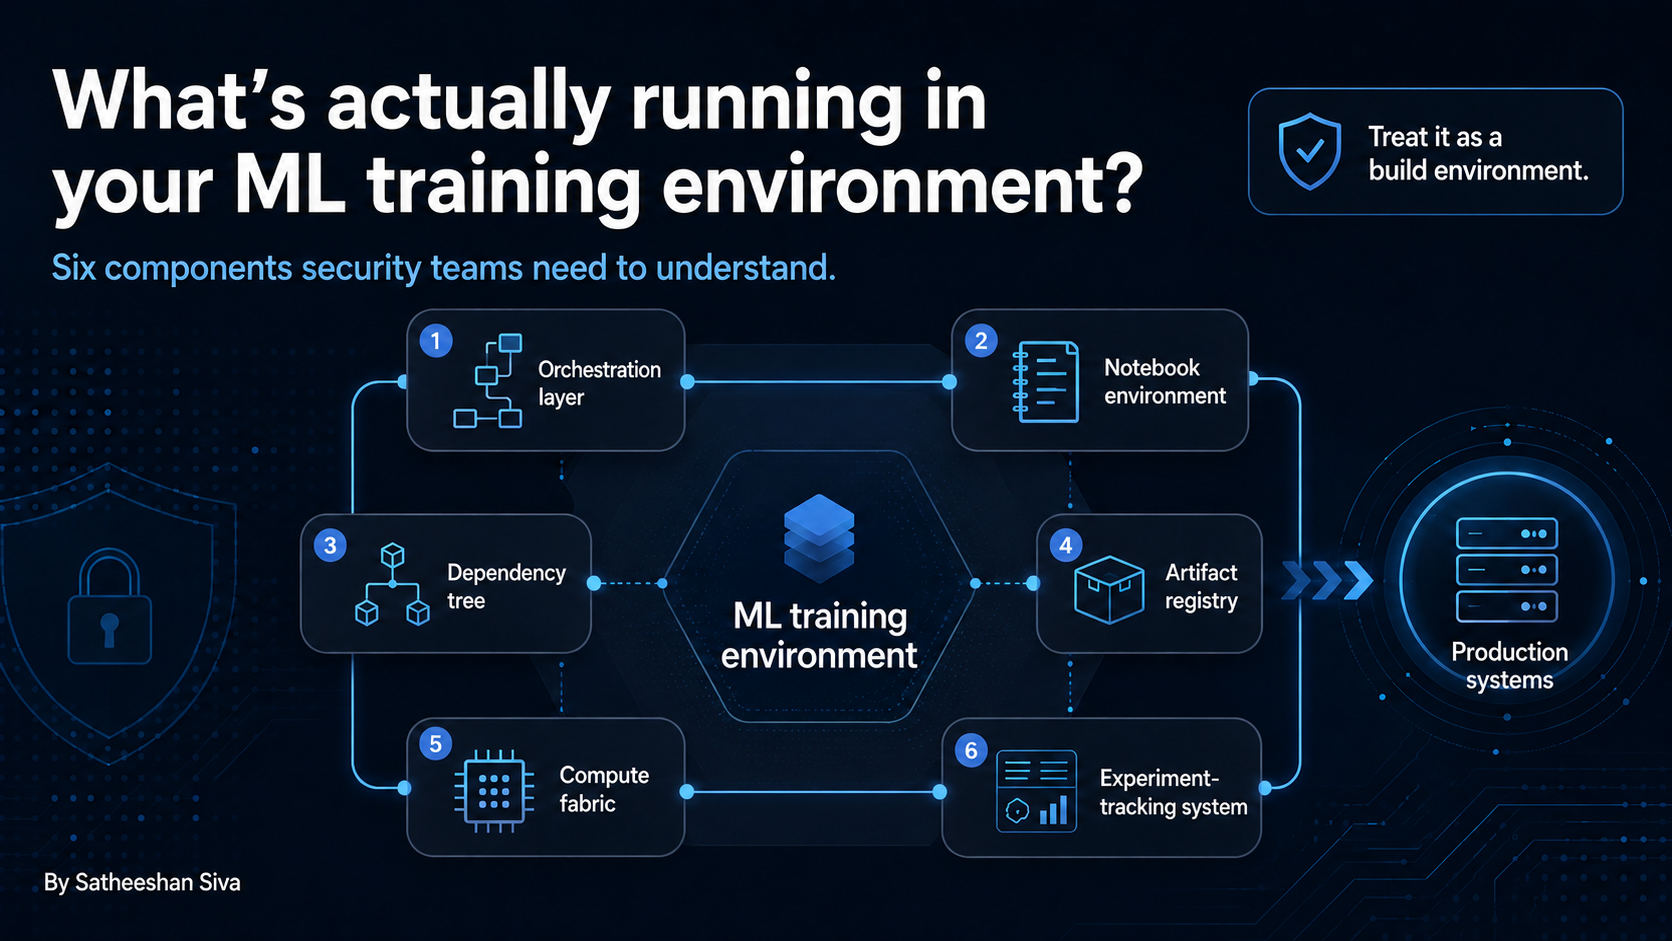
What’s actually running in your ML training environment?
Six components behind an ML training platform, the access they hold and why security teams should assess the environment as a software build pipeline.